Are we ready to respond?
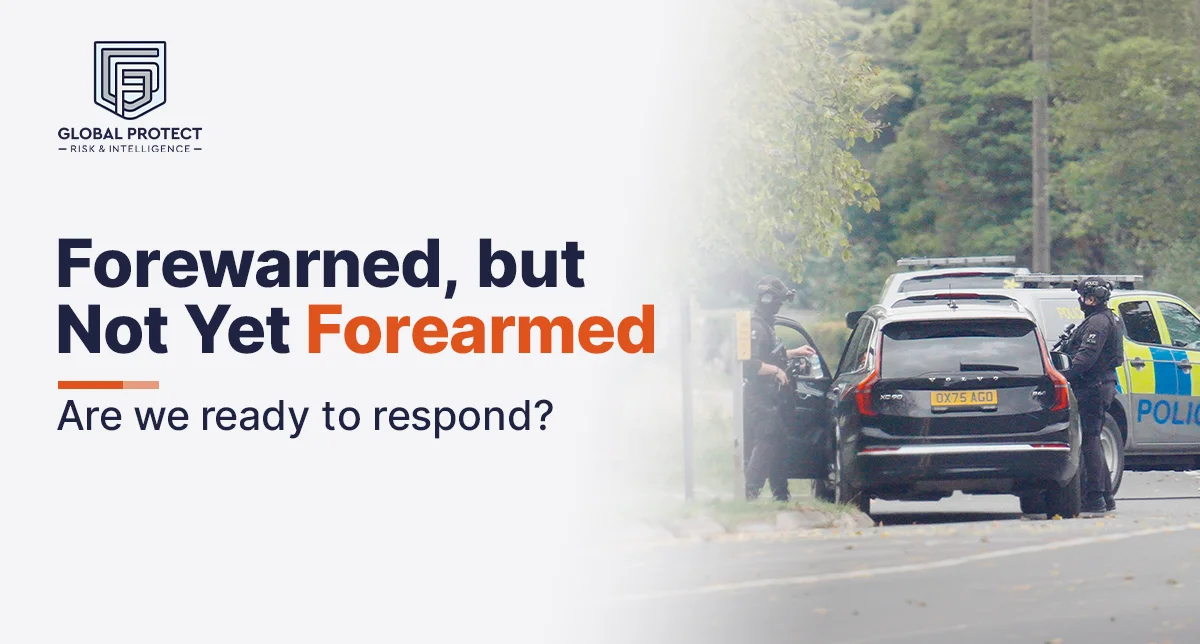
In the early hours of Sunday 27 September 2026, three vans were found on a country lane near RAF Fairford in Gloucestershire, the only heavy-bomber airfield the United States Air Force operates in Europe. Five men were arrested on suspicion of preparing acts of terrorism, a major incident was declared, and around 85 households were evacuated while bomb disposal teams examined the vehicles. By the following afternoon all five had been released on police bail without charge. Police later confirmed that no explosives were found in the vans, only a quantity of petrol. A sixth man was arrested in London on 1 October on suspicion of preparing terrorist acts. The prime minister has said there are strong indications that Iran played a part, while stressing that the police investigation is ongoing.
Two details matter to anyone responsible for a site. Police have said they were alerted by local residents, not by sensors or patrols. Neighbours were not moved for several hours. If that is how detection works around a USAF bomber base, it is worth asking what it looks like at an unmanned substation or a supplier’s warehouse. And days later, nobody outside the investigation can say what happened.
A third point holds whatever the investigation finds. Hostile reconnaissance does not stop at the fence. An incident of this kind, whether a genuine attempt, a rehearsal, or something else entirely, shows anyone watching how long the first response takes, how large the cordon is, who arrives, which roads close, and how long it takes to move the people nearby. Nothing is publicly known about what the men near Fairford intended, and nothing here suggests otherwise. The point is that a response played out in public is a response an adversary can study, and a dry run that draws it out costs far less than the real thing.
That is the condition every organization should plan for. Security measures try to prevent an incident. Business continuity exists for the moment prevention fails, and its job is to keep the organization running while the cause is still unknown. Yet most continuity planning, whether it protects a grid connection or a production line, carries a quiet assumption: that somebody will establish the cause reasonably quickly and that decisions can follow from that. Look at what has been happening across Europe and that assumption stops holding.
On 4 August 2026, staff at Leipzig/Halle Airport in Germany found a drone sitting next to a Ukrainian cargo aircraft. The drone was carrying explosives. It failed to function and a police bomb squad removed the detonator. The airport’s counter-drone system had not detected it arriving.
Less than four weeks later, on the night of 30 to 31 August, an individual wearing a balaclava climbed a fence at the WB Electronics plant in Skarzysko-Kamienna in Poland and planted an incendiary device. The plant, which makes drones for the Polish and Ukrainian armed forces, lost warehouse space to the fire. Prosecutors put the damage at a minimum of 15 million zloty, opened an investigation into foreign intelligence involvement, and classified it as a terrorist offence. A second fire hit an aircraft parts warehouse in Lublin within 24 hours.
The following day, the German government said Russia was responsible for Leipzig. It closed the Russian consulate in Bonn and the Russian House in Berlin. It also raised the national threat assessment from general to high. The interior minister put it plainly: Germany is not at war, but it is a daily target. In early September, improvised explosive devices were found at an electricity substation in Germany near the Polish border, and a second substation in the west of the country was attacked.
That is not a series of isolated incidents. It is a campaign that has been building for two years. In July 2024, an incendiary device hidden in a DHL parcel ignited at Leipzig/Halle Airport. It had been intended for onward air transport. According to German intelligence, only a flight delay prevented it from catching fire in the air. By 2026, prosecutors had linked the wider parcel campaign to Russian intelligence. Two years on, the same airport was again the site of an alleged Russian sabotage attempt. The method had changed but the target environment had not. Security adapts to the last incident while the adversary adapts to the response.
At sea the pattern is the same. On the last day of 2025, a fibre optic cable between Helsinki and Tallinn was disrupted, and Finnish authorities took control of a vessel and escorted it into port. That was one of a long run of Baltic incidents going back through Estlink 2, Balticconnector, and Nord Stream. In October 2025 the Eagle S prosecution, from an earlier Baltic cable case, was dismissed. The vessel had been identified and boarded. There was still no enforcement outcome.
That is the environment. Not an absence of evidence, but an absence of resolution.
From an adversary’s side of the table, that absence is itself the result. Drones flown over a dozen NATO states drew no collective response. The Eagle S case ended without an enforcement outcome. Anyone testing the system from outside draws the same conclusion: consequences are slow, uncertain, and often absent, while the cost of trying is low. Deterrence depends on the other side believing that a response will follow, and every probe that ends without one teaches them otherwise. Legal processes rightly move at the pace of evidence. As recent arrests near RAF Fairford followed by release on bail show, that pace is visible from outside, whatever the eventual outcome of a case.
It is an old burglar’s technique. Set off the intruder alarm, retreat, and wait. Do it again the next night and the night after. Eventually the keyholder decides the system is faulty, silences it, and goes back to bed. That is the night the building is entered. Grey-zone activity applies the same principle at national scale: each drone sighting noted and not answered, and each incident that fades without resolution, makes the next one easier to dismiss as a false alarm. The same happens inside a single organization. A site that has logged its tenth unexplained drone sighting or perimeter alarm is at risk of treating the eleventh as routine.
For operators, the practical consequence is that deterrence by prosecution cannot be part of the plan. Your own ability to respond is the part you control.
This is not a story about drones
It is easy to read all of this as an air defence problem or as a story about one airbase. It is neither. Whatever the Fairford investigation establishes about foreign involvement, the lesson does not depend on it. What connects a Gloucestershire airfield, a German airport, a Polish drone plant, two German substations, and a run of damaged Baltic cables is not the delivery method. It is the calculation behind it and the gap between an incident and anyone being able to define it.
Grey-zone action exploits that gap deliberately. It is damage calibrated to stay below the threshold that would force a military response, delivered so that attribution is slow, contested, and usually incomplete. A fire is an insurance claim until somebody proves otherwise. A drone over your site is a nuisance until it is something else.
The objective is rarely destruction. It is disruption, cost imposition, and a demonstration that the state cannot protect the systems and industries people depend on. Repeated disruption can erode confidence in state capability, deepen political friction, and weaken resilience long before anything physically fails.
The measure of how well this works is simple. Drones have been flown over NATO airspace, including over nuclear sites, repeatedly and in public. No collective response has followed.
Why infrastructure, why aerospace, and why the supply chain?
Five things make infrastructure operators and aerospace manufacturers attractive targets, and none of them is about the size of the asset or the finished aircraft.
Position beats size. The value of a target is where it sits, not how big it is. A distribution substation, a signalling installation, or a cable landing point can remove capacity far beyond its own footprint. Nobody needs to attack an aerospace prime contractor either. They need the sub-assembly, the composite, the sensor, or the warehouse that feeds the line. Disruption at tier two or tier three travels upward for a fraction of the risk, and the organization that suffers is frequently not the one that was attacked.
Deniability. Proxies are recruited through messaging apps and have no prior offending or intelligence background. In the United Kingdom, the first convictions under the National Security Act 2023 involved young men recruited via Telegram to burn a warehouse shipping goods to Ukraine, causing about a million pounds of damage. Your vetting covers your own staff and perhaps your contractors. It will not catch someone recruited last week from a local criminal group. Because the work is subcontracted in this way, the nationality of whoever carries it out says little about who is directing it.
Cost asymmetry. A drone costing a few thousand pounds can close an aerodrome for a day. An incendiary device costing less can remove warehouse capacity for months or destroy long-lead spares that take a year to replace. Defending against either can cost orders of magnitude more.
Fragmented ownership. UK infrastructure is privately owned, regulated sectorally, maintained by contractors, and interdependent across sector boundaries. Aerospace supply chains run through several tiers, and a prime contractor rarely has sight of physical security below the first. Nobody holds the whole picture. That is precisely the condition an adversary looks for.
Failure still counts. The Leipzig device did not detonate, and the attack still produced closed diplomatic missions, a raised national threat level, and a fortnight of headlines. Stoppage, evacuation, delay, suspended operations, and reputational damage all count as success.
What could a UK campaign look like?
The UK has arguably already witnessed the reconnaissance phase. From November 2024, drones were reported over American-operated bases at Lakenheath, Mildenhall, and Feltwell in Suffolk and Norfolk as well as over Fairford itself. The International Institute for Strategic Studies assessed in July 2026 that a coordinated drone campaign across a dozen NATO states between August 2024 and February 2026 was highly likely and that the incursions over the bases in Suffolk and Norfolk were among the earliest in the sequence. In November 2025 a Russian vessel directed lasers at RAF pilots tracking it.
The field of interested states is also widening. In July 2026, Iran’s Islamic Revolutionary Guard Corps publicly named Fairford’s use by US bombers and warned that any base used against Iran was a legitimate target. Hostile state interest in British sites is no longer a single-country problem.
The eastern counties of England alone hold a dense concentration of exactly the target types seen in Europe: aerospace and precision manufacturing, a defence intelligence establishment, American-operated airbases, regional aerodromes with thin counter-drone provision, a research base with heavy international exposure, and the power, water, and telecoms assets all of them depend on.
So, the planning scenario writes itself. Nothing here is exotic.
Someone reads your planning applications, capacity statements, outage notices, recruitment adverts, contractor case studies, and staff LinkedIn profiles. From them, they work out your shift patterns and who your key people are. Someone else, paid through an app and unaware who is really paying, drives past a substation, a depot, or a subcontractor warehouse a few times to test the perimeter. A drone flies over at night with its lights on, because being noticed is part of the effect.
Then a fire at a subcontractor warehouse or a contractor compound holding long-lead components, at night, when nobody is in and casualty risk is low. Or something happens during a planned outage or a switching operation. Or a telemetry link, a single maintenance provider, or the power feed to a factory or control facility goes down, which is the version most organizations never war-game because it is somebody else’s asset.
What follows is the real damage. An incident that sits between crime, aviation regulation, health and safety, sector regulation, and national security, yet fits none of your business continuity or crisis response plans cleanly. Weeks of not knowing what happened while you decide whether to keep operating and what to tell customers, regulators, and the public. Then a second event somewhere else in the same sector or supply chain, which is where the pattern becomes obvious and where a site-by-site response falls apart.
Recovery is then constrained not by engineering but by the availability of a specialist asset, vessel, or component that a whole sector or supply chain shares. The commercial cable repair market, for example, is structurally incentivized against holding surge capacity above routine fault rates. If several faults happen at once, your assumed restoration time may simply not exist. The same is true of a sole-source aerospace component with a year-long lead time.
Why your current posture will not hold
Site security in both sectors was built against theft, trespass, vandalism, protest, and ransomware. Those adversaries are opportunistic or financially motivated and resolve through familiar channels. State-directed action is different in a number of ways.
It targets the network or the supply chain rather than the node, so a perimeter assessment of one site tells you nothing useful. It exploits seams between teams, suppliers, contractors, regulators, and adjacent operators. It moves faster than your escalation route, because a 20-minute decision cannot wait for a monthly governance forum. It is specifically designed to defeat attribution. It is patient, so reconnaissance and action may be months apart and carried out by different people.
If your plan assumes the cause is known before decisions are needed, you are planning for a different threat.
The gap rarely tested
You cannot lawfully jam, spoof, or shoot down a drone over your own site in the United Kingdom. Detection buys you warning, not resolution.
Everything after detection depends on a decision chain that runs through your site security team or control room, your operations director, your suppliers and contractors, the aerodrome operator if there is one, the police, the sector regulator, and sometimes the Ministry of Defence. Very few organizations have ever run that chain end to end or tested whether a report from a member of the public, a supplier, or a neighbouring operator reaches someone with the authority to act at one o’clock on a Sunday morning. None of the European incidents gave anyone more than minutes to respond. That is the real gap, and it is not one that a procurement can close.
An adversary does not need to launch an attack to test that chain. A drone flown with its lights on, a vehicle left where it should not be, or a false report will show how long the response takes and where it breaks. Probing of this kind is established hostile reconnaissance practice, and it is cheap, deniable, and repeatable. If your response is slow or inconsistent, the rehearsal tells them so.
Fairford illustrates the edge of that chain. The outer ring around any site cannot be fenced, so it rests on patrols, liaison with the local force, and the attentiveness of neighbours, delivery drivers, and night-shift staff. Few organizations have a plan for telling those people anything, and a neighbourhood that feels its safety ranks below the fence will stop being vigilant on the site’s behalf.
Ten questions worth taking to your board
- Which single asset, supplier, or component, if lost tonight, would stop our line or turn an outage from hours into months?
- Who is allowed to halt operations or isolate plant on the basis of an unattributed drone sighting or an unexplained anomaly, and have they ever done it?
- How long would it take us to establish whether a fire or failure was deliberate, and what do we tell customers, the regulator, and the public meanwhile?
- What can an adversary learn about our sites, systems, suppliers, and staff from open sources in one working day?
- If a second incident hit a different site, supplier, or operator in our sector within 72 hours, who would connect the two, and how would we even hear?
- Do our contracts give us relief for a state-directed sabotage event, and do our insurers treat it as a covered loss or an act of war exclusion?
- What does our supplier and contractor onboarding ask about physical security, do we ever check the answer, and does anything oblige them to report reconnaissance that causes no loss?
- Which specialist repair asset or long-lead component do we share with the rest of our sector or supply chain, and what is the queue if several of us need it at once?
- If a neighbour rang one of our sites at one in the morning to report something suspicious, who would answer, who would call our named police contact, and who would warn the rest of the neighbourhood?
- When did we last exercise a scenario where the adversary was a state, the cause was unknown, and a second site was hit on day three?
If you cannot answer six of these, the problem is not in your risk register. It is in your operation.
The window
In 24 months Europe has gone from surveillance overflights, through airport closures and seabed interference, to an attempted explosive attack on a NATO airfield, confirmed arson at a drone manufacturer, and explosive devices at electricity substations. The cost of entry keeps falling.
British infrastructure and British aerospace have had the reconnaissance phase. Fairford has already shown what the first days of an incident near a protected site look like: detection by the public, a major incident, release on bail, and no confirmed cause. That is a window rather than a reprieve. The useful thing about a window is that you can decide what to do with it while it is still cheap.
Global Protect’s Fusion Hub provides continuous risk monitoring through tailored intelligence summaries, giving leadership teams and operators early warning of emerging threats, patterns, and supply chain and cross-sector dependencies, with risk scores that feed directly into OVRLAY.
Our OVRLAY GRC platform and BNDRY pen test programme turn that intelligence into practical assurance by identifying exposure and testing security and resilience arrangements. ROC Drill completes the process through realistic, intelligence-led red-team exercises that test whether plans, controls, and decision-making work under pressure, including across the seams with suppliers, contractors, regulators, and neighbouring operators.
Contact Global Protect Risk to discuss threat monitoring, assurance, and resilience testing tailored to your organization.
Frequently asked questions
What is grey-zone warfare?
Grey-zone warfare is hostile action deliberately kept below the threshold that would trigger an armed response, delivered so that attribution is slow and contested. It leaves the target country choosing between reacting on incomplete evidence and not reacting at all. Sabotage, arson, drone incursion, interference with undersea infrastructure, cyber attack, and disinformation are all used this way.
What does sub-threshold mean?
Sub-threshold means an act calculated to fall short of the point at which a state would treat it as an armed attack, and therefore short of the point that would trigger NATO Article 5 or a military response. The damage is real. The legal and political trigger is deliberately avoided.
Which infrastructure assets are most at risk?
Assets are chosen for their position rather than their size. Distribution-level and interface assets are the likely targets: substations, cable landing stations, signalling installations, pumping stations, telemetry links, and contractor compounds holding long-lead spares.
Why are aerospace suppliers targeted rather than prime contractors?
Because disruption at a supplier propagates upward at much lower risk. A tier-two or tier-three site holding sub-assemblies or long-lead components usually has thinner physical security than a prime contractor and produces the same effect on production.
Has the UK already been targeted?
The UK has seen drone incursions over American-operated airbases in Suffolk, Norfolk, and Gloucestershire from November 2024, a Russian vessel directing lasers at RAF pilots tracking it in November 2025, and a Russia-directed arson attack on a warehouse in east London that produced the first convictions under the National Security Act 2023. Separately, a major incident was declared near RAF Fairford in September 2026. The prime minister has said there are strong indications of Iranian involvement, but the investigation is ongoing and no one had been charged at the time of writing.
Could a suspicious incident be a test of our response?
Yes. Dry runs and deliberate probing are established hostile reconnaissance techniques. A suspicious vehicle, a drone, or a false report can be used to measure response times, cordon sizes, and escalation routes before any real attack. Unexplained incidents that cause no loss should be treated as intelligence, recorded, and reviewed for what they would have revealed to an observer. The danger is that repeated false alarms train a site to stop responding, which may be exactly what they were for.
Who carries out these attacks?
Frequently they are locally recruited proxies rather than intelligence officers. Recruitment often happens through messaging platforms such as Telegram, and the person carrying out the act may not know who is ultimately paying. This is what makes both vetting and attribution difficult. It is also why a suspect’s nationality says little about who, if anyone, was directing them.
How long does attribution usually take?
Weeks to months, and sometimes it never produces an enforcement outcome. Germany took roughly a month to attribute the Leipzig airport incident publicly. Polish investigations into the WB Electronics fire were opened immediately but remain ongoing. The Eagle S prosecution over Baltic cable damage was dismissed in October 2025 despite the vessel being identified and boarded. Organizations should plan to make operating decisions before they know what happened.
Can a UK organization jam or bring down a drone over its own site?
No. Private operators in the United Kingdom cannot lawfully jam, spoof, or bring down a drone, even over their own property. Detection provides warning only, and resolution depends on the police and sometimes on the Ministry of Defence or central government.
Why does undersea infrastructure keep being targeted?
Because attribution is hardest at sea, where a civilian vessel provides plausible cover and jurisdiction is contested. NATO responded with Baltic Sentry in 2025 and the European Commission introduced a subsea infrastructure package worth 347 million euros, with a Cable Security Toolbox, in February 2026.
Why might restoration take longer than our continuity plan assumes?
Because specialist repair capacity and long-lead components are often shared across a sector or supply chain, and those markets have no incentive to hold surge capacity above routine demand. Restoration times based on a single isolated fault may not survive several concurrent ones.
What should a business continuity plan include for this threat?
A plan for this kind of scenario should identify which critical roles, suppliers, and assets create single points of failure, name deputies and hold current handover packs, define who owns rapid decisions and on what evidence, record whether contracts provide relief, and be exercised rather than filed.
Does an unsuccessful attack still count as a success for the attacker?
Yes. The Leipzig device failed to detonate, and the attack still achieved diplomatic expulsions, a raised national threat level, and sustained media attention. Disruption and demonstration of reach are the objectives, not destruction.
What is the first practical step?
Map which single external dependency would stop production or extend an outage from hours to months if it were lost tonight. Then establish who is authorized to act in an ambiguous incident, whether they have ever done it, and whether a report from a member of the public would reach them at night. None of these answers requires a procurement.
Sources
• Police probe ‘terror’ incident near RAF base used for Iran war: What we know, Al Jazeera
• Five men arrested over suspected RAF Fairford terror plot all UK nationals in 20s, ITV News
• British police find no explosives in vans linked to 5 men detained near U.S.-run military base, PBS NewsHour
• UK-Iranian dual national arrested in London over RAF Fairford incident, The Irish Times
• Germany blames Russia for drone attack on Leipzig airport, CNN
• German government blames Russia for Leipzig airport drone attack, Defense News
• Poland opens terror probe into fire at factory supplying Ukraine drones, Al Jazeera
• Polish drone plant fire undoubtedly arson, says Tusk, Notes from Poland
• Poland suspects sabotage behind fires at plants linked to drone production, Brussels Signal
• Seabed zero: Baltic sabotage and the global risks to undersea infrastructure, Bulletin of the Atomic Scientists
• The silent front: cable crisis in the Baltic Sea, Atlas Institute
• Russia highly likely behind drone incursions over US bases in England, The War Zone on the IISS assessment
• UK sends anti-drone troops to Belgium as airports shut down, CBS News
• How the CPS used National Security Act legislation to prosecute the Ukrainian aid warehouse plot, Crown Prosecution Service
• Understanding the suspected terror plot near RAF Fairford, Outside the Wire, Black Widow Security (Substack), 28 September 2026